Skip to content
View lbarrosby's full-sized avatar

Block or report lbarrosby

Block user

Prevent this user from interacting with your repositories and sending you notifications. Learn more about blocking users.

You must be logged in to block users.

Content in all repositories owned by your account will be closed.
Maximum 250 characters. Please don’t include any personal information such as legal names or email addresses. This note will only be visible to you.
Report abuse

Contact GitHub support about this user’s behavior. Learn more about reporting abuse.

Report abuse
lbarrosby/README.md

Lucas Barros

Platform engineering on Kubernetes

Platform engineer based in Rio de Janeiro. I design and operate Kubernetes platforms for teams that ship to production every day, mostly in financial services.

Over the last years that meant running a fleet of 330 clusters behind ArgoCD, Atlantis and Rancher, turning EKS provisioning from a two-day manual process into a 40-minute Terraform/Terragrunt pipeline, moving a 3,000 jobs/day Jenkins farm to immutable infrastructure, and treating cloud cost as an engineering metric rather than a finance report.

I care about boring, predictable infrastructure: everything in code, every change reviewed, upgrades that nobody notices.

Open source

Contributing upstream across the cloud native ecosystem: CNCF projects like Kubernetes, Envoy, Prometheus, Argo, Crossplane, Headlamp and CoreDNS, plus Terraform providers, Helm charts and AI infrastructure tooling (NVIDIA device plugin, Ray, deepwiki-open).

Upstream PRs Merged Projects

Merged

In review

Project Pull requests
terraform-aws-modules/terraform-aws-eks fix: Remove unused cluster_primary_security_group_id from eks_managed_node_groups type
knative/eventing fix(apiserversource): drop deleted ApiServerSources from the tracker
fix(trigger): track the subscriber with the Trigger as observer
kubecolor/kubecolor fix: match -o json and -o yaml case-insensitively like kubectl
fix: honor =false on --no-headers, --watch, --follow and --interactive
prometheus-community/helm-charts [prometheus-pingdom-exporter] Fix ServiceAccount annotations indentation
[prometheus-sql-exporter] Fix indentation of serviceAccount annotations and networkPolicy labels
[prometheus-mysql-exporter] Honor cloudsqlproxy.image.pullPolicy
[prometheus-adapter] Fix service annotations indentation
[prometheus-nats-exporter] Render extraContainers in the Deployment
[prometheus-systemd-exporter] Render env values in the DaemonSet
[alertmanager-snmp-notifier] Honor namespaceOverride on all resources
kyverno/policies fix(psp-migration-mpol): mutate Pods only in add-apparmor, add-capabilities and add-runtimeClassName
lima-vm/lima downloader: don't leave a partial file at the local path
limatmpl: strip native arch aliases from image-derived instance names
guestagent: don't run kubectl when no kubeconfig is found
kyverno/kyverno fix(dpol): resolve wildcard apiGroups and apiVersions against discovery
deliveryhero/helm-charts [stable/dregsy]: fix podLabels value name and render it on Deployment pods
[stable/prometheus-cloudflare-exporter]: render podLabels on the pod template
[stable/kubecost-reports-exporter]: use the chart service account and render scheduling values
kubernetes-sigs/cluster-api-provider-aws 🐛 fix(eks): resolve sourceSecurityGroupRoles in additional control plane ingress rules
🐛 fix(eks): handle nil taint key and value in TaintsFromSDK
kubernetes-sigs/external-dns refactor(validation): return field.ErrorList from config validators
openebs/zfs-localpv fix(rbac): limit zfs controller access to namespaces to read-only
fix(helm): render zfsNode and zfsController updateStrategy
jenkinsci/helm-charts fix(jenkins): read the documented controller.clusterIP value
fluent/fluent-operator fix(helm): honor buffer.enable in the Fluentd outputs
fix(helm): use the buffer scope in the Fluentd OpenSearch output
fix(helm): honor logstashFormat: false in the Fluentd ES and OpenSearch outputs
terraform-aws-modules/terraform-aws-ecs fix: Pass cluster_capacity_providers_wait_duration through the root module
stackrox/kube-linter fix(pdb-min-available): match deployments with matchExpressions selectors
kubernetes-sigs/kustomize Make sure ResetOpenAPI() is called in tests, even if the tests failed
external-secrets/external-secrets fix(bitwarden): honor name.regexp in GetAllSecrets find
kubernetes-sigs/aws-load-balancer-controller feat: add opt-in --leader-election-lease-duration flag
feat(helm): make failurePolicy configurable for TargetGroupBinding, IngressClassParams and pod server id webhooks
fix(helm): quote default-tags and aws-vpc-tags args
kubernetes-sigs/dra-example-driver Remove the temp checkpoint file when writing the checkpoint fails
aminueza/terraform-provider-minio fix(replication): change a rule's target bucket on the same endpoint
fix(replication): set the ID before removing unused remote targets
falcosecurity/falcosidekick fix(handlers): skip outputs whose client was not created
karmada-io/karmada fix(resourceinterpreter): skip Ingress TLS entries without secretName in dependencies
etcd-io/auger Skip tombstone revisions when listing key summaries
dapr/components-contrib fix(state/redis): return empty results instead of an error when a query matches nothing
projectcontour/contour Set alt_stat_name for DNS name clusters
DataDog/integrations-extras Add vLLM Production Stack integration
Add Volcano integration
Add Hugging Face TEI integration
Add llama.cpp integration
kubernetes-sigs/aws-ebs-csi-driver Honor leaderElection values for csi-resizer and allow lease tuning in the chart schema
argoproj/argo-helm fix(argocd-image-updater): mount the secret created by certificateSecret
fix(argo-cd): render server.service.externalIPs as a list
fix(argocd-image-updater): Allow webhook port in NetworkPolicy when service.enabled is set
sergelogvinov/proxmox-csi-plugin docs: explain why volume snapshots need the root@pam password
goharbor/terraform-provider-harbor fix(#650): retention policy replaced on every plan when scope is a plain project ID
tsuru/terraform-provider-tsuru fix: reject malformed import IDs for tsuru_cluster_pool and tsuru_pool_constraint
fix: report non-API errors from retried tsuru calls
feat: add tsuru_pool data source
fix: drop tsuru_app_cname and tsuru_app_router from state when removed outside terraform
fluent/fluentd record_accessor: raise ConfigError for a non-integer array index
tsuru/nginx-operator fix: don't panic updating an ingress when nginx sets no ingress annotations
scaleway/terraform-provider-scaleway fix: #4587 accept offer-specific private network options on baremetal servers
tsuru/deploy-agent fix: return an error instead of panicking on a truncated build context archive
tsuru/charts fix(tsuru-prometheus-pool): select pods by the release's Prometheus name
coredns/coredns plugin/acl: only add the EDE OPT record when the request has EDNS
plugin/header: keep rules from every header block
openebs/lvm-localpv fix(chart): render lvmNode and lvmController labels
openobserve/openobserve-helm-chart fix(openobserve,openobserve-standalone): pass group, kind and port to HTTPRoute parentRefs
fix(openobserve): honor postgres.spec.enableSuperuserAccess
tsuru/tsuru-client fix(metadata): accept the -t type in any case
chore(docker): bump runtime image to alpine 3.24.3
fix: print an empty JSON array for empty lists with --json
tsuru/tsuru fix(api): return 400 when creating a team token with an invalid token_id
ci: pin third-party actions to commit SHAs and restrict token permissions
fix(api): return 409 when creating a team token with an existing token_id
Mongey/terraform-provider-kafka Support importing kafka_quota
vultr/terraform-provider-vultr Mark credential attributes as sensitive
Remove database sub-resources from state when the database is gone
digitalocean/terraform-provider-digitalocean spaces: remove bucket CORS configuration from state when it is gone
kubernetes-sigs/cluster-inventory-api access: sort profile-sourced exec env vars by name
access: do not modify the provider exec config
exoscale/terraform-provider-exoscale fix(block_storage_volume_snapshot): remove from state when deleted outside of Terraform
kubernetes-sigs/e2e-framework conditions: wait for observed generation in DaemonSetReady
utils: use go env to find the go install directory
watcher: stop the event loop when the watch ends
cert-manager/cert-manager fix(pki): accept lowercase attribute type names in literalSubject
metallb/metallb config: detect duplicate BGPPeers that only differ by name
stakater/Reloader fix(handler): treat non-2xx --webhook-url responses as failures
aws/aws-cli Write JSON file cache entries atomically
cloudflare/cfssl signer: trim spaces and skip empty entries in SplitHosts
awslabs/eks-node-viewer fix: update node usage when a bound pod's requests change
bitnami/sealed-secrets fix(kubeseal): fail on malformed documents instead of skipping them
fix(helm): use the container ports in the NetworkPolicy ingress rule
istio/istio gateway: honor exportTo when resolving Hostname backendRefs
otwld/ollama-helm fix: keep service ipFamilies inside the non-Knative Service
fix: allow revisionHistoryLimit to be set to 0
kubernetes-sigs/kwok heap: update the key when pushing an existing item
open-webui/helm-charts fix(terminals): match operator labels in default terminalPodSelector
aziontech/lib fix(utils): keep '=' in cookie values in parseRequest
fix(utils): treat paths with a dot in a parent segment as routes
fix(cookies): emit Max-Age=0 when maxAge is 0
fix(cookies): keep '=' in cookie values when parsing
runatlantis/atlantis fix: read pre-v0.44.0 pull records with int policy approvals
fix: reject targeted plan for a missing dir before creating its status
MagaluCloud/mgc-sdk-go fix(client): let errors.Is/As see the error wrapped by RetryError
fix(http): always send the request when MaxAttempts is zero or negative
MagaluCloud/terraform-provider-mgc fix(blockstorage): remove volume from state when it no longer exists
fix(vm): remove instance from state when it no longer exists
ansible-collections/community.proxmox fix(proxmox_kvm): return newid when the clone target already exists
bpg/terraform-provider-proxmox fix(acme): remove dns plugin from state when deleted outside terraform
fix(vm): read back usb4 and higher host USB devices
hetznercloud/hcloud-go fix(exp): escape backslashes in TXT records and keep escapes in one chunk
hetznercloud/terraform-provider-hcloud fix(server): do not delete primary ip already assigned to the server
helmfile/helmfile fix: keep elements added to an existing array by --state-values-set
aws-ia/terraform-aws-eks-blueprints-addons fix: Keep nested prefixes in the Velero backup location
kubernetes-sigs/descheduler fix(helm): allow setting serviceMonitor.honorLabels to false
NVIDIA/k8s-device-plugin Inspect embedded config.map entries before adding SYS_ADMIN
terraform-aws-modules/terraform-aws-iam fix: Keep IRSA policy count known when policy documents are not read
fix: Add ec2:DescribeVpcPeeringConnections to the LBC TargetGroupBinding only policy
github-aws-runners/terraform-aws-github-runner fix(termination-watcher): keep retry queue visibility timeout at or above the Lambda timeout
kubernetes-sigs/jobset helm: default the ServiceMonitor client cert to the release's metrics secret
equinix/terraform-provider-equinix fix: remove equinix_fabric_connection from state when it no longer exists
fix: mark Fabric credential attributes as sensitive
fix: stop mutating the shared Network Edge client user agent
terrakube-io/terrakube-helm-chart fix(otel): quote defaulted values in the otel ConfigMaps
fix(api): render automountServiceAccountToken when it is false
AsyncFuncAI/deepwiki-open fix(docker): actually install certificates from CUSTOM_CERT_DIR
fix: use the shared WebSocket URL helper in slides and workshop pages
tsuru/kubernetes-router ci: pin third-party actions to commit SHAs and restrict token permissions
fix(ingress): remove certificate without panicking when ingress has multiple TLS entries
tsuru/go-tsuruclient fix(config): keep token files readable only by the owner
tsuru/rpaas-operator fix: return the get error before using the rpaas instance in reconcile
tsuru/acl-operator fix: stop requeueing deleted tsuru apps and cronjobs
coredns/helm fix: default the server port when it is not set
goharbor/harbor-helm feat(core): add core.existingSecretKey for the core secret
memcached/memcached contrib: add a Helm chart
flant/shell-operator [shell-operator] feat: add a generic Helm chart
gruntwork-io/terragrunt fix: include init in get_terraform_commands_that_need_vars for OpenTofu >= 1.8
ray-project/ray [Java] Bump log4j to 2.25.5 and jackson-databind to 2.18.11
argoproj-labs/terraform-provider-argocd feat(account_token): add optional token_id attribute
stern/stern fix: compile the highlight regexp once per tail
goharbor/harbor fix: return 404 for role ids outside the int32 range
argoproj/argo-cd feat(health): add health checks for Strimzi KafkaMirrorMaker and KafkaMirrorMaker2 (#5048)
fix(cli): include argocd-cmd-params-cm in admin export/import (#9506)
fix(cli): report server version as unavailable in core mode (#9747)
kubernetes-sigs/headlamp frontend: resourceMap: Use targetRefs for backend policy relations
open-feature/java-sdk-contrib fix(flagd): stop the FlagStore streamer thread on shutdown
litmuschaos/litmus fix(authentication): check the stored role before letting an owner leave
openkruise/charts fix(kruise): point CRD conversion webhooks at the chart webhook service
openebs/dynamic-localpv-provisioner fix(helm): render localpv.securityContext on the provisioner container
kube-logging/fluent-plugin-label-router Add worker_id label to router metrics with multiple workers
submariner-io/submariner-charts Omit ceIPSecPSK when no IPsec PSK is set
carvel-dev/vendir Explain when a github release has no assets to fetch
kube-vip/kube-vip fix(services): do not treat DHCP placeholder VIPs as shared
konveyor/tackle2-hub 🐛 Validate shared api.Document fields against their schema
crossplane/crossplane test(e2e): cover CRD hand-off for control planes upgraded from v1.20
open-policy-agent/java-opa-sdk fix(cli): print counters and histograms in the metrics table
kubernetes/website [pt-br] Add tasks/configure-pod-container/configure-projected-volume-storage.md
[pt-br] Add tasks/configure-pod-container/attach-handler-lifecycle-event.md
[pt-br] Add tasks/configure-pod-container/configure-pod-initialization.md
[pt-br] Add tasks/configure-pod-container/pull-image-private-registry.md
[pt-br] Add tasks/configure-pod-container/assign-cpu-resource.md
[pt-br] Add tasks/configure-pod-container/configure-liveness-readiness-startup-probes.md
[pt-br] Add tasks/configure-pod-container/assign-memory-resource.md
[pt-br] Add concepts/architecture/leases.md
prometheus/alertmanager ui: stop building a Brotli variant of index.html
envoyproxy/gateway fix(status): merge policy ancestor status across controllers
docs: move Gateway Exported Metrics from Tasks to Concepts
prometheus/node_exporter fix(diskstats): drop sector metrics on darwin

Projects

  • helm-charts: production-ready Helm charts with secure defaults, Gateway API, HPA/KEDA and schema-validated values, tested and released from CI
  • terraform-aws-platform: opinionated Terraform modules for EKS platforms (VPC, EKS with access entries and Pod Identity, Karpenter), tested with mock providers and laid out for Terragrunt

LinkedIn Email Profile views


Certifications

CKA Terraform Associate AWS Solutions Architect Associate Calico Operator eBPF VMware Double VCP AWS Cloud Practitioner Azure Fundamentals

Platform   Kubernetes EKS Rancher Envoy Istio Cilium

Delivery   Terraform Atlantis Argo CD Helm Jenkins GitHub Actions Ansible

Observability   Prometheus Grafana Datadog

Cloud & code   AWS Azure GCP Go Python Linux


Profile details

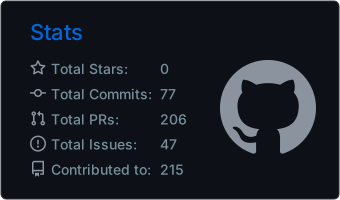
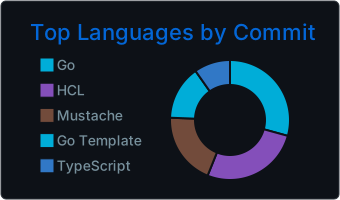
Stats Languages Streak

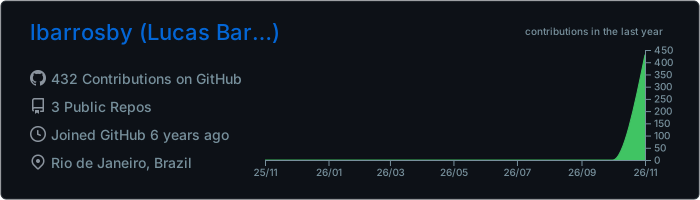
Contributions

Popular repositories Loading

  1. lbarrosby lbarrosby Public

    Profile README

  2. gateway gateway Public

    Forked from envoyproxy/gateway

    Manages Envoy Proxy as a Standalone or Kubernetes-based Application Gateway

    Go

  3. atlantis atlantis Public

    Forked from runatlantis/atlantis

    Terraform Pull Request Automation

    Go

  4. helm-charts helm-charts Public

    Production-ready Helm charts: secure defaults, Gateway API, HPA/KEDA, PDB, topology spread, schema-validated values and tested in CI

    Go Template

  5. node_exporter node_exporter Public

    Forked from prometheus/node_exporter

    Exporter for machine metrics

    Go

  6. cilium cilium Public

    Forked from cilium/cilium

    eBPF-based Networking, Security, and Observability

    Go