Repository navigation
Migrate 10 Sentinel solutions to Defender XDR (v3.2.2) - #15368
idoshabi07 wants to merge 12 commits into
Conversation


- Microsoft PowerBI (3.2.2)
- Azure SQL Database solution for sentinel (3.2.2)
- Business Email Compromise - Financial Fraud (3.2.2)
- AzureDevOpsAuditing (3.2.2)
- SOC-Process-Framework (3.2.2)
- AzureSecurityBenchmark (3.2.2)
- Dev 0270 Detection and Hunting (3.2.2)
- Google Cloud Platform Audit Logs (3.2.2)
- GoogleWorkspaceReports (3.2.2)
- AtlassianJiraAudit (3.2.2)

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: ce1d21a4-1e05-48fd-bc25-8d15e6ec3765


 Alon Karmona (alon-karmona1)
left a comment
Alon Karmona (alon-karmona1)
left a comment
There was a problem hiding this comment.
nice
 v-atulyadav
added
Solution
 Ofer Inbar (oferInbar)
added
1P Solution

|
Hi idoshabi07 , I see for Atlassian Jira Audit, Azure SQL database solution, Azure Devops Auditing, Business Email compromise and Dev 0270 Detection solution the date Modified in release notes is added "20-04-2026" rather than "20-10-2026". Can you please check if that is correct date, if not please update the release note dates for these solutions. Thanks. |
Correct v3.2.2 release dates from April 20 to October 20, 2026.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: df20c9b2-5f2b-40ec-963e-f5775eae4416
Preserve the document title as alert custom details instead of emitting an invalid name-only File entity. Rebuild the existing 3.2.2 package without changing the detection query or account mapping.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Give the privileged password-change rule a distinct name, alert title, and accurate description in source and XDR content. Preserve IDs and KQL, update source provenance, and rebuild the solution at the approved version 3.2.3.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Preserve decoded deployment values while supporting ARM-TTK identifier checks and nested template extraction. Keep validation checks unchanged.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>

Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Preserve failed candidate history and all normal validation gates. Retain exact structural receipt bytes across platform line endings.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>

Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Keep the DNS zone custom detail and remove a mapping that lacks DNS server and host address evidence. Prepare the approved 3.2.3 release.

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>

Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
…AzureDevOpsAuditing 3.2.2

Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119
Co-authored-by: Copilot <223556219+Copilot@users.noreply.github.com>
Copilot-Session: 3f74d2f7-43ee-4e47-b6aa-3b7e839a1119

There was a problem hiding this comment.
🟡 Changes recommended
Critical detection execution, telemetry coverage, and prerequisite defects remain unresolved, along with moderate workbook-link defects.
12 open issues


What changed in this PR
Migrates ten Microsoft Sentinel solutions toward hybrid Sentinel and Defender XDR delivery, primarily at version 3.2.2, with selected follow-up fixes at 3.2.3. Also updates shared packaging, migration tests, and validation tooling.
Changes:
- Adds Custom Detections and Defender workbook selections alongside existing Sentinel content.
- Updates solution metadata, attribution, release notes, and migration configuration.
- Revises ARM identifier and JSON serialization handling, evidence comparison, and local/CI validation.
Unresolved findings include critical detection execution, telemetry coverage, and prerequisite defects, plus moderate workbook-link defects. Generated Package/ artifacts are listed for completeness but were excluded from review.
| File | Description |
|---|---|
Tools/SentinelToXDRMigration/tests/test_version_policy.py |
Adds identifier and ARM serialization regression coverage. |
Tools/SentinelToXDRMigration/tests/test_parser_bindings.py |
Updates packaged provenance expectations. |
Tools/SentinelToXDRMigration/tests/test_content_deployment_parameters.py |
Updates packaged identifier and provenance expectations. |
Tools/SentinelToXDRMigration/solution_manager/packaging/packaging_selection.py |
Compares structural evidence semantically while retaining byte hashes. |
Tools/SentinelToXDRMigration/agent-workflows/end-to-end-migration.md |
Documents replacing unaccepted release candidates. |
Tools/Create-Azure-Sentinel-Solution/V3/README-V3_1.md |
Documents ARM-compatible identifiers and JSON serialization. |
Tools/Create-Azure-Sentinel-Solution/common/customDetections.ps1 |
Centralizes ARM identifier projection and brace escaping. |
Tools/Create-Azure-Sentinel-Solution/common/commonFunctions.ps1 |
Updates analytic bindings, watchlist handling, and package serialization. |
Solutions/SOC-Process-Framework/XDR Workbooks/Building_a_SOCSmallStaff.json |
Adds the small-staff Defender workbook. |
Solutions/SOC-Process-Framework/XDR Workbooks/Building_a_SOCPartTimeStaff.json |
Adds the part-time-staff Defender workbook. |
Solutions/SOC-Process-Framework/XDR Workbooks/Building_a_SOCMediumStaff.json |
Adds the medium-staff Defender workbook. |
Solutions/SOC-Process-Framework/XDR Workbooks/Building_a_SOCLargeStaff.json |
Adds the large-staff Defender workbook. |
Solutions/SOC-Process-Framework/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/SOC-Process-Framework/ReleaseNotes.md |
Records workbook migration. |
Solutions/SOC-Process-Framework/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/SOC-Process-Framework/data/Solution_Soc-Process.json |
Selects four XDR workbooks and updates the release. |
Solutions/Microsoft PowerBI/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/Microsoft PowerBI/ReleaseNotes.md |
Records workbook migration and release history. |
Solutions/Microsoft PowerBI/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/Microsoft PowerBI/Package/createUiDefinition.json |
Generated artifact; excluded from review. |
Solutions/Microsoft PowerBI/Data/Solution_Microsoft PowerBI.json |
Selects the XDR activity workbook. |
Solutions/GoogleWorkspaceReports/XDR Detections/GWorkspaceDifferentUAsFromSingleIP.yaml |
Adds user-agent anomaly detection. Critical: references the unsupported workspace-saved GWorkspaceActivityReports parser; inline its normalization or query underlying tables, and declare actual inputs. |
Solutions/GoogleWorkspaceReports/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/GoogleWorkspaceReports/ReleaseNotes.md |
Records Custom Detection migration. |
Solutions/GoogleWorkspaceReports/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/GoogleWorkspaceReports/Data/Solution_GoogleWorkspaceReports.json |
Selects ten XDR detections. |
Solutions/Google Cloud Platform Audit Logs/SolutionMetadata.json |
Adds attribution and version 3.2.3 metadata. |
Solutions/Google Cloud Platform Audit Logs/ReleaseNotes.md |
Records migration and the DNS mapping correction. |
Solutions/Google Cloud Platform Audit Logs/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/Google Cloud Platform Audit Logs/Data/Solution_GCPAuditLogs.json |
Selects seven XDR detections. |
Solutions/Dev 0270 Detection and Hunting/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/Dev 0270 Detection and Hunting/ReleaseNotes.md |
Records Custom Detection migration. |
Solutions/Dev 0270 Detection and Hunting/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/Dev 0270 Detection and Hunting/Package/createUiDefinition.json |
Generated artifact; excluded from review. |
Solutions/Dev 0270 Detection and Hunting/Data/Solution_DEV0270.json |
Selects four XDR detections. |
Solutions/Business Email Compromise - Financial Fraud/XDR Detections/migration-config.yaml |
Adds migration mappings, exclusions, and scoped review decisions. |
Solutions/Business Email Compromise - Financial Fraud/SolutionMetadata.json |
Adds attribution and version 3.2.3 metadata. |
Solutions/Business Email Compromise - Financial Fraud/ReleaseNotes.md |
Records migration and the file-entity mapping correction. |
Solutions/Business Email Compromise - Financial Fraud/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/Business Email Compromise - Financial Fraud/Package/createUiDefinition.json |
Generated artifact; excluded from review. |
Solutions/Business Email Compromise - Financial Fraud/Data/Solution_Business Email Compromise - Financial Fraud.json |
Selects six XDR detections and updates branding. |
Solutions/AzureSecurityBenchmark/Workbooks/AzureSecurityBenchmark.json |
Changes SimuLand links. Moderate: the image targets an HTML landing page, and the heading no longer opens the advertised guidance; restore a direct image and specific article link. |
Solutions/AzureSecurityBenchmark/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/AzureSecurityBenchmark/ReleaseNotes.md |
Records the posture-change Custom Detection. |
Solutions/AzureSecurityBenchmark/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/AzureSecurityBenchmark/Package/createUiDefinition.json |
Generated artifact; excluded from review. |
Solutions/AzureSecurityBenchmark/Data/Solution_AzureSecurityBenchmark.json |
Selects the XDR posture-change detection. |
Solutions/AzureDevOpsAuditing/XDR Detections/AzDOHistoricPrPolicyBypassing.yaml |
Adds historical policy-bypass detection. Critical: both branches omit ADOAuditLogs_CL and its normalization, losing events and distorting history. Critical: prerequisites omit the queried AzureDevOpsAuditing table; reconcile workload and connector records. |
Solutions/AzureDevOpsAuditing/XDR Detections/AzDOAdminGroupAdditions.yaml |
Adds administrator-group monitoring. Critical: replacing the parser drops declared ADOAuditLogs_CL events; inline both inputs and ActionId normalization, then refresh evidence. |
Solutions/AzureDevOpsAuditing/XDR Detections/ADOSecretNotSecured.yaml |
Adds unsecured-variable detection. Critical: omits the declared custom-table branch and normalization, missing its events; restore complete inline parser logic and provenance. |
Solutions/AzureDevOpsAuditing/XDR Detections/ADORetentionReduced.yaml |
Adds retention-reduction detection. Critical: never reads declared ADOAuditLogs_CL; restore complete parser logic or explicitly normalize the custom table and regenerate evidence. |
Solutions/AzureDevOpsAuditing/XDR Detections/ADOPATUsedWithBrowser.yaml |
Adds browser PAT-use detection. Critical: reads only the legacy table, omitting declared custom-table events; inline both inputs and normalization, then regenerate provenance. |
Solutions/AzureDevOpsAuditing/XDR Detections/ADONewExtensionAdded.yaml |
Adds extension-installation detection. Critical: drops declared ADOAuditLogs_CL events; restore the parser union and normalization and refresh evidence. |
Solutions/AzureDevOpsAuditing/XDR Detections/ADOMaliciousToolingDetections1.yaml |
Adds malicious-tooling detection. Critical: excludes ADOKit activity in declared ADOAuditLogs_CL; restore complete parser logic or explicitly normalize that input and regenerate evidence. |
Solutions/AzureDevOpsAuditing/XDR Detections/ADOAuditStreamDisabled.yaml |
Adds audit-stream-disable detection. Critical: omits declared custom-table events and can fail without the legacy table; inline the complete union and normalization. |
Solutions/AzureDevOpsAuditing/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/AzureDevOpsAuditing/ReleaseNotes.md |
Records migration of eighteen detections. |
Solutions/AzureDevOpsAuditing/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/AzureDevOpsAuditing/Data/Solution_AzureDevOpsAuditing.json |
Selects XDR detections and updates source paths. |
Solutions/Azure SQL Database solution for sentinel/SolutionMetadata.json |
Adds attribution and release metadata. |
Solutions/Azure SQL Database solution for sentinel/ReleaseNotes.md |
Records Custom Detection migration. |
Solutions/Azure SQL Database solution for sentinel/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/Azure SQL Database solution for sentinel/Package/createUiDefinition.json |
Generated artifact; excluded from review. |
Solutions/Azure SQL Database solution for sentinel/Data/Solution_AzureSQLDatabasesolutionforsentinel.json |
Selects ten XDR detections. |
Solutions/AtlassianJiraAudit/XDR Detections/JiraPrivilegedUserPasswordChanged.yaml |
Adds privileged-user password-change detection. Critical: both branches reference unsupported workspace-saved JiraAudit; inline its raw-table union and normalization in both branches and regenerate evidence. |
Solutions/AtlassianJiraAudit/SolutionMetadata.json |
Adds attribution and version 3.2.3 metadata. |
Solutions/AtlassianJiraAudit/ReleaseNotes.md |
Records migration and the naming correction. |
Solutions/AtlassianJiraAudit/Package/testParameters.json |
Generated artifact; excluded from review. |
Solutions/AtlassianJiraAudit/Data/Solution_AtlassianJiraAudit.json |
Selects ten XDR detections. |
Solutions/AtlassianJiraAudit/Analytic Rules/JiraPrivilegedUserPasswordChanged.yaml |
Corrects rule naming and description and increments its version. |
.script/local-validation/run-arm-ttk.ps1 |
Uses shared ARM-TTK parameters and result filtering. |
.script/local-validation/README.md |
Documents shared local/CI ARM-TTK exemptions. |
.github/workflows/kql-validations.yaml |
Updates the validation SDK to .NET 8. |
.github/instructions/packaging.instructions.md |
Documents revised ARM-TTK behavior. |
.github/actions/entrypoint.ps1 |
Applies shared ARM-TTK parameters and filtering in CI. |
.github/actions/Dockerfile |
Includes the shared ARM-TTK filter in the validation image. |
Review effort: Balanced
| displayName: Azure DevOps Audit Stream Disabled | ||
| status: disabled | ||
| queryCondition: | ||
| queryText: 'AzureDevOpsAuditing |
| displayName: Azure DevOps Audit Detection for known malicious tooling | ||
| status: disabled | ||
| queryCondition: | ||
| queryText: 'AzureDevOpsAuditing |
| queryCondition: | ||
| queryText: 'let allowed_publishers = dynamic([]); | ||
|
|
||
| AzureDevOpsAuditing |
| displayName: Azure DevOps PAT used with Browser | ||
| status: disabled | ||
| queryCondition: | ||
| queryText: 'AzureDevOpsAuditing |
| displayName: Azure DevOps Administrator Group Monitoring | ||
| status: disabled | ||
| queryCondition: | ||
| queryText: "// Change to true to monitor for Project Administrator adds to *any* project\nlet MonitorAllProjects = false;\n// If MonitorAllProjects is false, trigger only on Project Administrator add for the following projects\nlet ProjectsToMonitor = dynamic(['<project_X>','<project_Y>']);\nAzureDevOpsAuditing\n| where Area == \"Group\" and OperationName == \"Group.UpdateGroupMembership.Add\"\n| where Details has 'Administrators'\n| where Details has \"was added as a member of group\" and (Details endswith '\\\\Project Administrators' or Details endswith '\\\\Project Collection Administrators')\n| parse Details with AddedIdentity ' was added as a member of group [' EntityName ']\\\\' GroupName\n| extend Level = iif(GroupName == 'Project Collection Administrators', 'Organization', 'Project'), AddedIdentityId = Data.MemberId\n| extend Severity = iif(Level == 'Organization', 'High', 'Medium'), AlertDetails = strcat('At ', TimeGenerated, ' UTC ', ActorUPN, '/', ActorDisplayName, ' added\ |
| requiredWorkloads: | ||
| - workload: sentinel | ||
| dataTypes: | ||
| - ADOAuditLogs_CL |
| displayName: Azure DevOps Pull Request Policy Bypassing - Historic allow list | ||
| status: disabled | ||
| queryCondition: | ||
| queryText: "let starttime = 14d;\nlet endtime = 3h;\n// Add full UPN (user@domain.com) to Authorized Bypassers to ignore policy bypasses by certain authorized users\nlet AuthorizedBypassers = dynamic(['foo@baz.com', 'test@foo.com']);\nlet historicBypassers = AzureDevOpsAuditing\n| where TimeGenerated between (ago(starttime) .. ago(endtime))\n| where OperationName == 'Git.RefUpdatePoliciesBypassed'\n| distinct ActorUPN;\nAzureDevOpsAuditing\n| where TimeGenerated >= ago(endtime)\n| where OperationName == 'Git.RefUpdatePoliciesBypassed'\n| where ActorUPN !in (historicBypassers) and ActorUPN !in (AuthorizedBypassers)\n| parse ScopeDisplayName with OrganizationName '(Organization)'\n| project TimeGenerated, ActorUPN, IpAddress, UserAgent, OrganizationName, ProjectName, RepoName = Data.RepoName, AlertDetails = Details, Branch = Data.Name,\n BypassReason = Data.BypassReason, PRLink = strcat('https://dev.azure.com/', OrganizationName, '/', ProjectName, '/_git/', Data.RepoName, '/pullrequest/',\ |
| "type": 1, | ||
| "content": { | ||
| "json": "### 💡 [SimuLand for Attack Simulation](https://www.microsoft.com/security/blog/2021/05/20/simuland-understand-adversary-tradecraft-and-improve-detection-strategies/)\r\n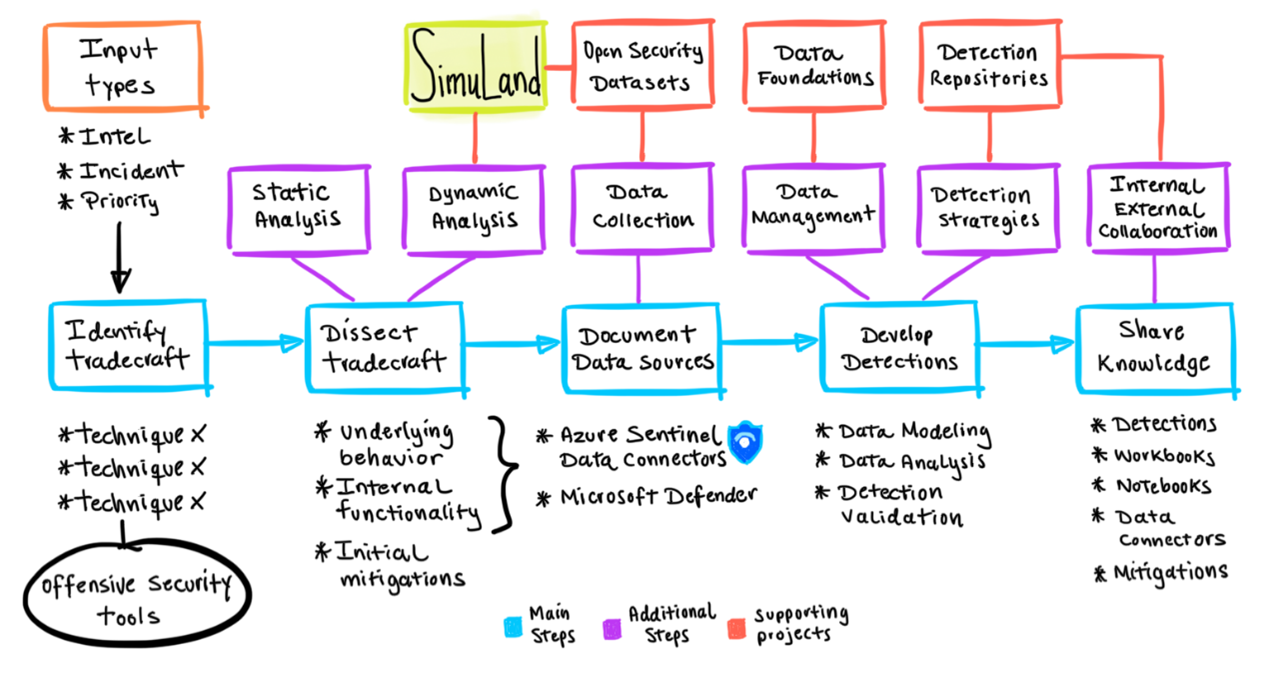 \r\n" | ||
| "json": "### 💡 [SimuLand for Attack Simulation](https://www.microsoft.com/en-us/security/blog/)\r\n \r\n" |


Microsoft PowerBI (3.2.2)
Azure SQL Database solution for sentinel (3.2.2)
Business Email Compromise - Financial Fraud (3.2.2)
AzureDevOpsAuditing (3.2.2)
SOC-Process-Framework (3.2.2)
AzureSecurityBenchmark (3.2.2)
Dev 0270 Detection and Hunting (3.2.2)
Google Cloud Platform Audit Logs (3.2.2)
GoogleWorkspaceReports (3.2.2)
AtlassianJiraAudit (3.2.2)
Required items, please complete
Change(s):
Reason for Change(s):
Version Updated:
Testing Completed:
Checked that the validations are passing and have addressed any issues that are present:
Guidance <- remove section before submitting
Before submitting this PR please ensure that you have read the following sections and filled out the changes, reason for change and testing complete sections:
Thank you for your contribution to the Microsoft Sentinel Github repo.
Change(s):
Reason for Change(s):
Version updated:
Testing Completed:
Note: If updating a detection, you must update the version field.
Checked that the validations are passing and have addressed any issues that are present:
Note: Let us know if you have tried fixing the validation error and need help.